SOC 2 Type II in 12 months. Predictable, within your tools.

The standard that US customers and enterprise buyers expect from cloud and technology providers. We take you to an attested report without any additional compliance software.

Message
Learn more
Do we need a US audit firm?

SOC 2 reports are issued under the AICPA attestation standards. The examination must be performed by a licensed CPA firm – this can also be a European audit firm holding the appropriate licensure.

We recommend suitable auditors and coordinate the audit.

Type I or straight to Type II?

A Type I report attests to the design of controls as of a specific date and is available immediately after the readiness phase. A Type II report demonstrates operating effectiveness over an observation period and is what enterprise customers typically require.

If you need to secure an active deal, start with Type I; if time allows, go straight into the observation period.

How long should the observation period be?

Typically 3 to 12 months. The first report is often scoped at 3 to 6 months to deliver results quickly. Subsequent reports usually cover 12 months.

You determine the length together with the auditor.

We are ISO 27001 certified – how much can be reused?

Most of it. The SOC 2 Security criteria largely overlap with the ISO 27001 Annex A controls. Risk assessment, policies, access controls and supplier management can be adopted directly.

The main additions are the system description and ongoing evidence collection.

What does a SOC 2 project cost?

The effort depends on the scope, the selected criteria and your starting point. Following the gap analysis, you receive a fixed price for the readiness phase.

The CPA firm’s audit fees are contracted separately. There are no recurring software license fees.

Your Path to the Report
Four phases, one management system. Evidence is generated where your team already works.
READINESS
< 2 Months
OBSERVATION PERIOD
3-12 Months
Additional software
None
Weeks 1–8
Readiness
Gap analysis, scope and system description, policies, control implementation.
Weeks 9-10
Type I
The auditor attests to the design of controls as of the report date.
Months 3-12
Observation
Controls operate in day-to-day business. Evidence is generated in Jira, Microsoft 365 and your cloud console.
Thereafter
Type II
Operating effectiveness attested over the period. The report goes to your customers.
SOC 2
5 Reasons
for
SOC 2
with
Heartland

Readiness in less than 2 months

A fixed project plan with milestones instead of an open-ended advisory engagement. From day one, you know when the audit can take place.

SOC 2 readiness in less than 2 Months with a fixed project plan
SOC 2 evidence generated directly in Jira, Confluence, Microsoft 365, AWS or Azure

Evidence in your tools

Jira, Confluence, Microsoft 365, AWS or Azure – evidence is generated where your team works. No additional portal.

No ongoing costs

No software subscription required. We extend your existing system landscape instead of licensing a compliance platform.

SOC 2 without ongoing compliance software costs
Coordination with the CPA firm through to the SOC 2 report

Auditor coordination

We recommend suitable CPA firms, prepare the evidence package and support you through the auditor’s inquiries until the report is issued.

One system for ISO 27001 and SOC 2

Shared controls, shared evidence, one management system. The second standard costs a fraction of the first.

One management system for ISO 27001 and SOC 2
Our SOC 2 Implementation
Work becomes evidence.
Evidence becomes the report.
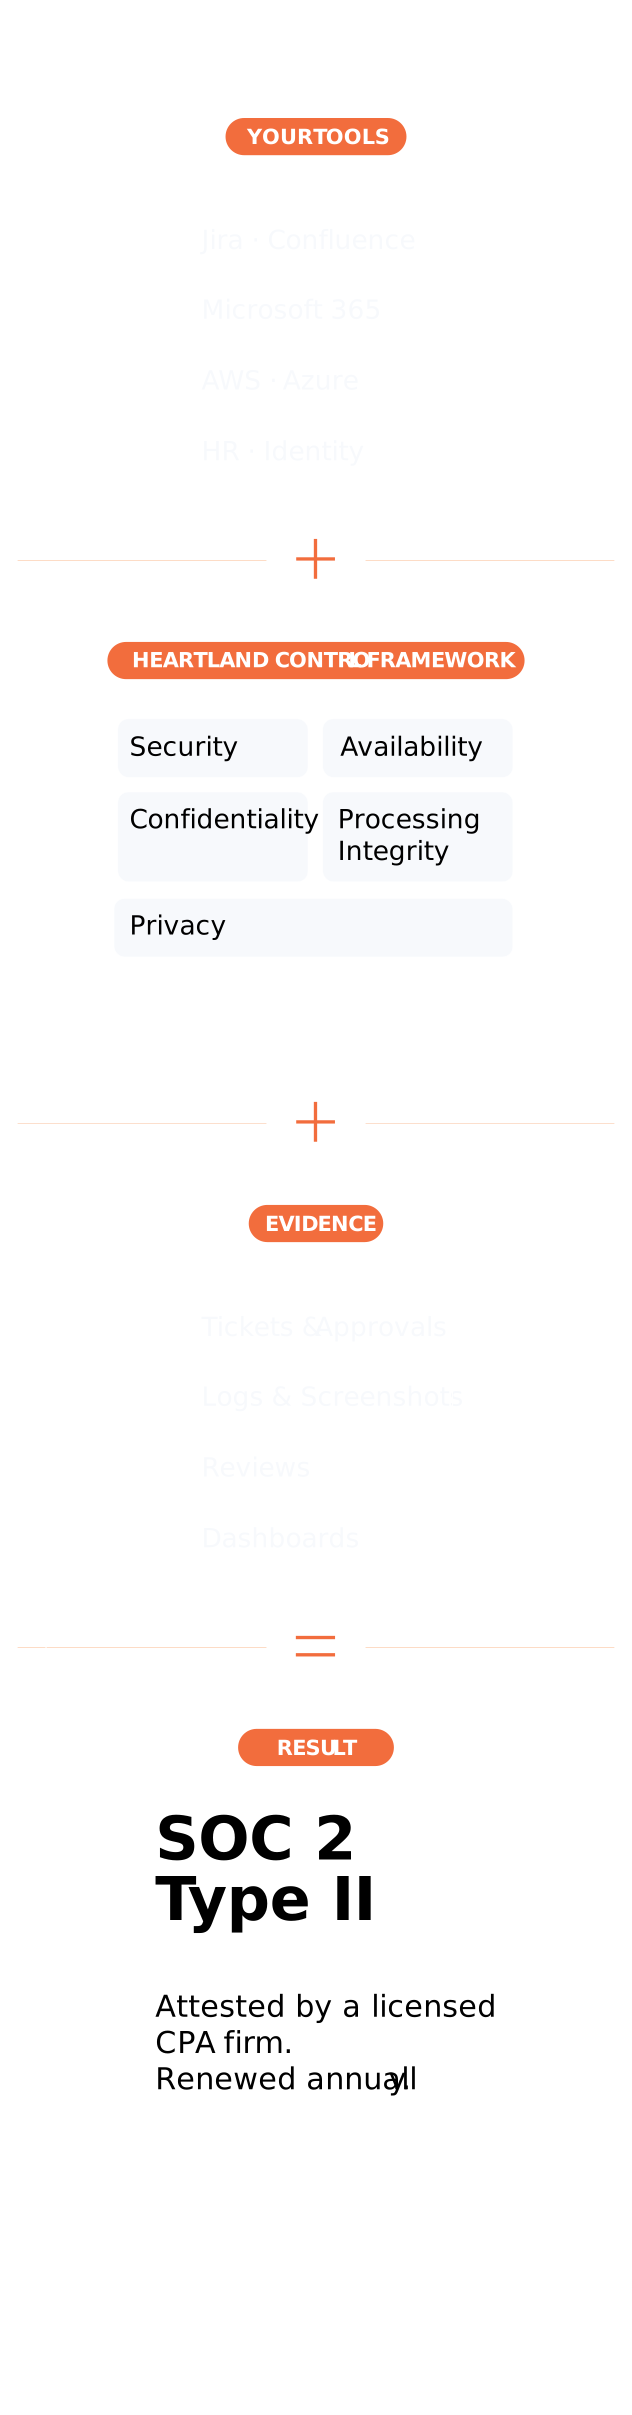
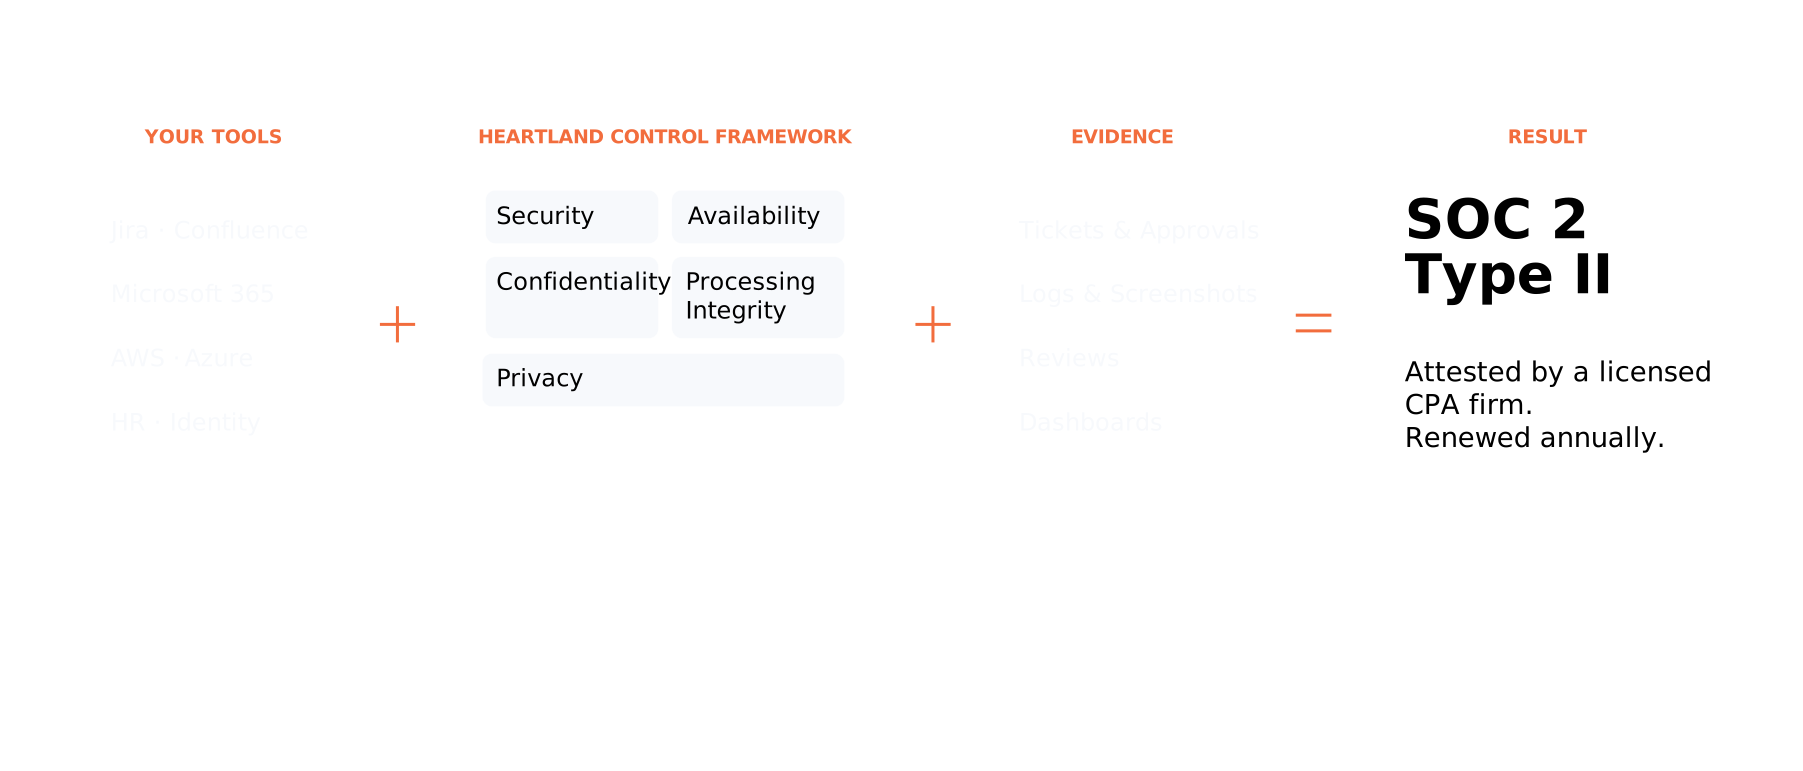
Your tools provide the evidence. Our control framework maps it to the Trust Services Criteria. The auditor receives a structured evidence package.
SOC 2 implementation: evidence from your tools is mapped to the Trust Services Criteria through the Heartland control framework, resulting in a SOC 2 Type II report
FEATURED SUCCESS STORY
Polarise – from ISMS to C5:2026
Time-to-Certification
3 months
Lead Advisory
ISMS & Audit
Certification
ISO 27001
ISO 9001
Read Case Study
Learn more
Your Measurable Value
Intelligent processes, transparency and less manual effort – as with every Heartland management system.
A. Integration of existing tools
Controls as workflows in SharePoint, Jira or Confluence.
B. Automated workflows
Reminders, approvals and escalations run on predefined rules.
C. Transparency through dashboards
Real-time control status for management and auditors.
D. PDCA cycle on autopilot
Type II year after year, without starting over.
Heartland solutions
Your partner for future-proof management systems and SOC 2.