BSI Cloud Computing Compliance Criteria Catalogue · For Data Centres

C5:2026

Cloud security evidence for data centres and cloud providers — attested by auditors and built on existing management systems.

ISO 27001 as the Basis for the C5 Attestation
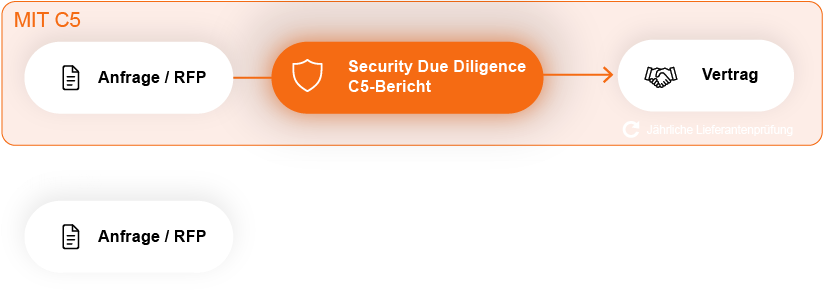
ISO 27001 as the Basis for the C5 Attestation
C5 requires an ISMS conforming to ISO/IEC 27001 (OIS-01), and the sharpening additional criterion even requires a valid certification. An existing certificate covers the core but replaces no C5 criterion: cloud-specific hardening, tenant separation, transparency information and customer controls come on top.

Heartland brings both together in one control system — built once, evidenced many times.

What Changes with C5:2026

C5:2026 replaces C5:2020: 168 criteria across 17 areas, plus 6 General Conditions on law, availability, subservice organisations and data locations. New are the Shared Security Responsibility Model, threat intelligence, confidential computing and container management as well as stricter requirements for identities, cryptography and development.

Anyone starting now builds directly on C5:2026.

Implementing C5 with Heartland

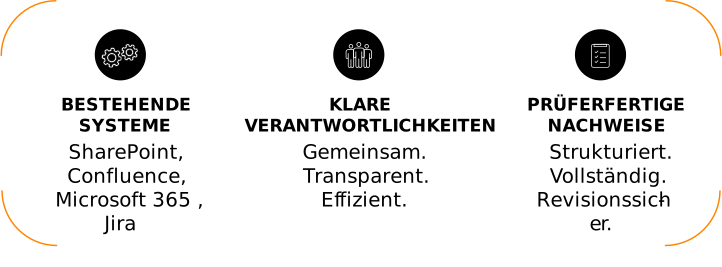
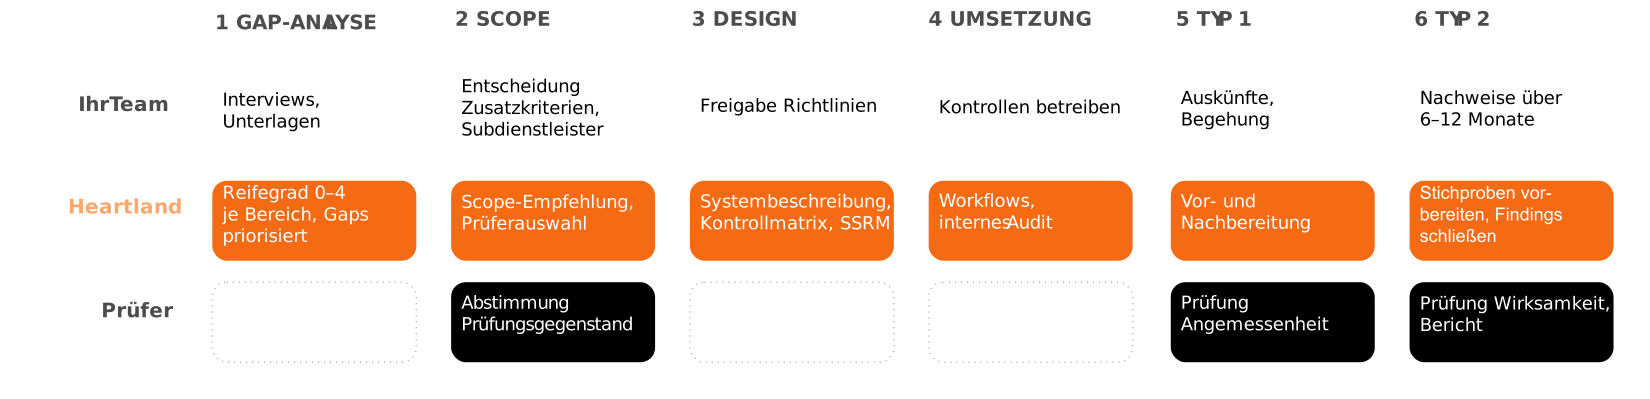
Heartland builds the control system inside your existing tool landscape: documentation in SharePoint or Confluence, workflows in Microsoft 365 or Jira, no second data set and no platform lock-in. From the gap analysis through scope and system description to the coordination with the auditor, one contact stays responsible.

Evidence is created where the work already happens — year after year.

Effort and Cost of a C5 Attestation

The cost consists of two separate items: the consulting effort for building the system and producing evidence, and the auditor’s fee for Type 1 and Type 2. The consulting effort depends on the service model, the scope and how far your ISMS already carries — the Heartland Approach adds no additional licences.

In the C5 readiness check we quantify both before you decide.

C5
Drei Nachweise,
drei Ebenen,
ein Management­system.
C5 setzt ein ISO-27001-konformes ISMS voraus; die DIN EN 50600 liefert die Infrastruktur-Nachweise.
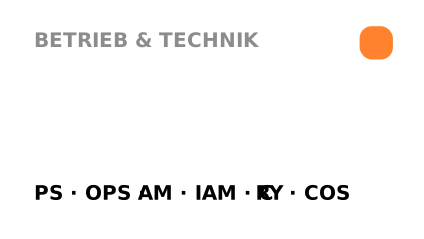
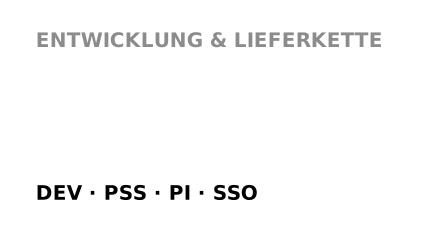
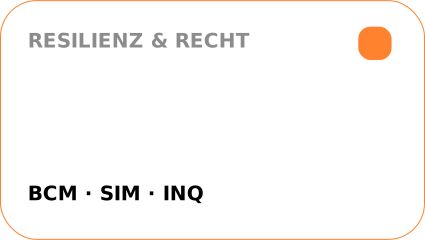
DIE 17 KRITERIENBEREICHE – WER LIEFERT DEN NACHWEIS
PS
OPS
BCM
BCM
SP
HR
AM
SSO
SIM
COM
COM
CRY
COS
PI
DEV
PSS
INQ
GC
>
DIN EN 50600 liefert
>
ISO 27001 deckt ab
>
C5-spezifisch – bauen wir mit Ihnen auf
DER MASSSTAB
Der Kriterienkatalog C5:2026
168 Kriterien in 17 Bereichen – was der Wirtschaftsprüfer sehen will. Kein Zertifikat, sondern ein Testat: Ob ein Kriterium erfüllt ist, entscheidet der Prüfer.
168
17
6
3
Kriterien
Kriterienbereiche
Kriterienarten: Basis · AS · AC
General Conditions
Transparenzangaben: Recht, SLAs, Subdienstleister, Datenlokationen · Neu in 2026: Shared Security Responsibility Model, korrespondierende Kundenkriterien
Der Heartland C5 Approach
Ihr C5-System.
Dort, wo Ihr Team
arbeitet.
Wir bauen die Anforderungen, Kontrollen und Nachweise in Ihre bestehenden Systeme und Workflows ein - von der Gap-Analyse bis zum Testat.

5 Gründe für Heartland

Ein Kontrollsystem für C5, ISO 27001 und DIN EN 50600

Einmal nachweisen, mehrfach nutzen.

Keine Zusatzsoftware

Wir arbeiten in Ihren bestehenden Tools und Systemen.

Ein Ansprechpartner bis zum Bericht

Von der Gap-Analyse bis zur Abstimmung mit dem Prüfer.

Heartland NIS-2 ISMS - Umfassende SIcherheit
Heartland NIS-2 ISMS - Software Freiheit
Heartland NIS-2 ISMS - Neue Wertschöpfung
Heartland NIS-2 ISMS -  keine Folgekosten
Heartland NIS-2 ISMS - in weniger als 4 Monaten

Prüferperspektive von Anfang an

Wir bauen das, was der Wirtschaftsprüfer sehen will – nicht mehr, nicht weniger.

Rechenzentrums-Erfahrung

DIN EN 50600 und ISO 27001 für Colocation- und AI-Rechenzentren.
FEATURED SUCCESS STORY
Polarise – vom ISMS zum C5:2026
Time-to-Certification
3 Monate
Lead Advisory
ISMS & Audit
Certification
ISO 27001
ISO 9001
Read Case Study
Learn more
DAS HERZSTÜCK DES HEARTLAND APPROACHS
Workflow Automatisierung
Regelbasierte Abläufe erzeugen die Nachweise, die der Prüfer im Betrachtungszeitraum sehen will: Zutrittsreviews, Rezertifizierungen, Notfalltests, Ticket-Stichproben. Aufgaben und Prüfungen laufen in Microsoft 365, Jira oder vergleichbaren Plattformen – revisionssicher, Jahr für Jahr. Wir integrieren Compliance-Prozesse in Ihre bestehenden Systeme statt eine Plattform zu lizenzieren.
Heartland solutions
Your partner for quality management in critical infrastructure.