BSI C5 · For Data Centres

C5:2026

The cloud security attestation for data centers – attested by an independent auditor, built on your management system.

Prerequisite for enterprise and hyperscaler customers
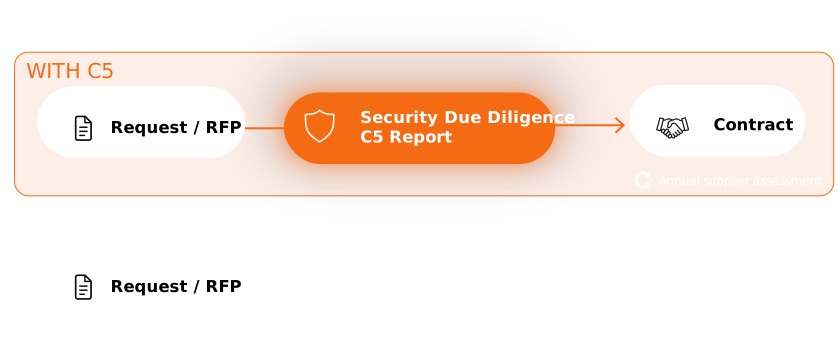
Sales process with and without a C5 attestation: with a C5 report, security due diligence leads to a contract – without C5, no contract
ISO 27001 as the foundation of the C5 attestation

C5 requires an ISMS that conforms to ISO 27001 (OIS-01); the additional, more stringent criterion even requires a valid certification. An existing certification covers the core but does not replace any C5 criterion: cloud-specific hardening, tenant isolation, transparency disclosures and customer controls come on top.

Heartland brings both together in a single control system – built once, evidenced many times.

What Changes with C5:2026

C5:2026 supersedes C5:2020: 168 criteria across 17 domains, plus 6 General Conditions covering legal matters, availability, subservice organizations and data locations. New additions include the Shared Security Responsibility Model, threat intelligence, confidential computing and container management, along with stricter requirements for identities, cryptography and development.

Organizations starting now build directly on C5:2026.

Implementing C5 with Heartland

Heartland builds the control system within your existing tool landscape: documentation in SharePoint or Confluence, workflows in Microsoft 365 or Jira – no second data repository and no platform lock-in. From gap analysis through scoping and the system description to alignment with the auditor, one point of contact remains accountable.

Evidence is generated where the work already happens – year after year.

Effort and cost of a C5 attestation

Costs consist of two separate items: the advisory effort for implementation and evidence management, and the auditor’s fee for the Type 1 and Type 2 reports. The advisory effort depends on the service model, the scope and how far your existing ISMS already carries you – the Heartland Approach involves no additional licenses.

In our C5 Readiness Check, we quantify both before you decide.

C5
THE Heartland C5 Approach
Your C5 system. Right where your team works.
We embed the requirements, controls and evidence into your existing systems and workflows – from gap analysis to attestation.
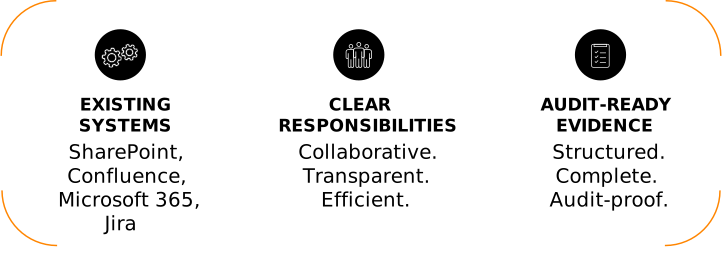
Heartland C5 Approach: existing systems, clear responsibilities and audit-ready evidence
In your tools
SharePoint, Confluence, Microsoft 365, Jira
No lock-in
No second data repository, no platform dependency.
One point of contact
From the gap analysis to the auditor.
Annual evidence
Within the normal workflow, year after year.
In your tools
SharePoint, Confluence, Microsoft 365, Jira
No lock-in
No second data repository, no platform dependency.
One point of contact
From the gap analysis to the auditor.
Annual evidence
Within the normal workflow, year after year.
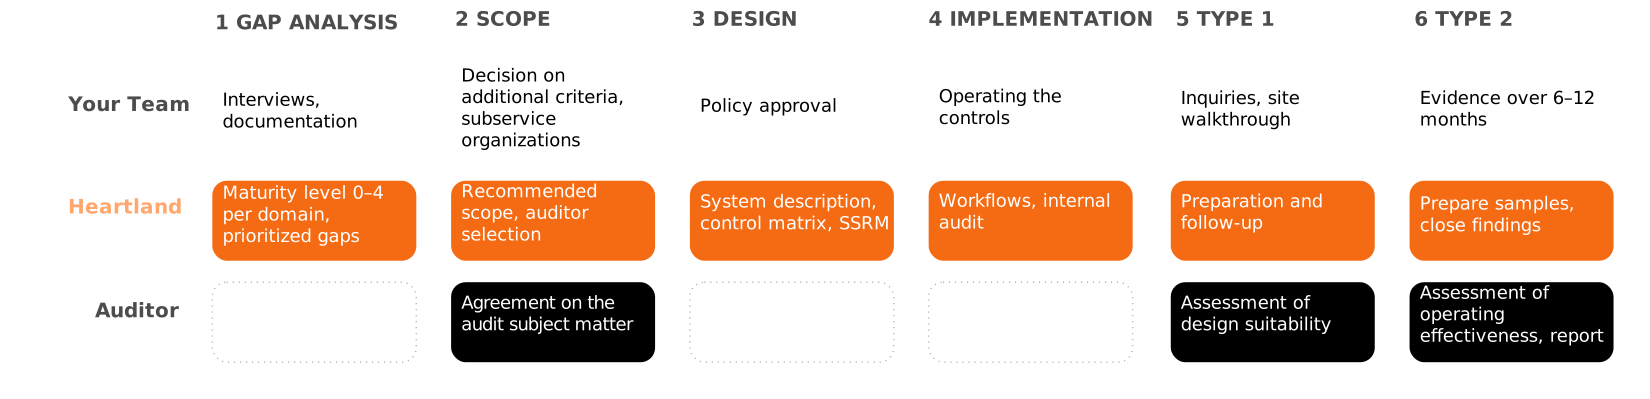
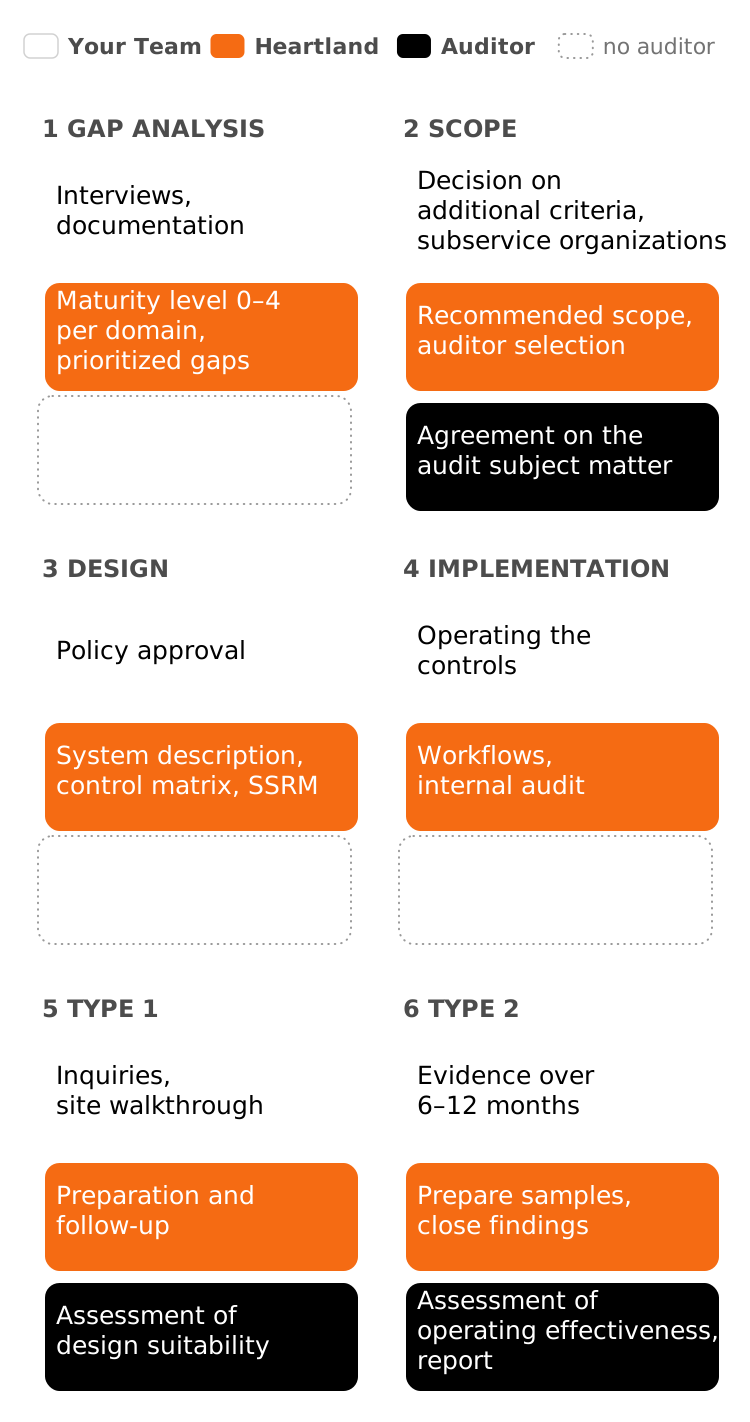
C5 attestation process in six phases – gap analysis, scope, design, implementation, Type 1 and Type 2 – with the roles of the customer, Heartland and the auditor
Ablauf zum C5-Testat in 6 Phasen – Gap-Analyse, Scope, Design, Umsetzung, Typ 1 und Typ 2 – mit Aufgaben von Kunde, Heartland und Prüfer
The Core of the Heartland Approach
Evidence created in everyday work
Rule-based workflows generate the evidence the auditor expects to see during the review period: access reviews, recertifications, contingency tests, ticket samples. Tasks and checks run in Microsoft 365, Jira or comparable platforms – audit-proof, year after year. We integrate compliance processes into your existing systems instead of licensing a platform.
Cost comparison: the Heartland Approach with no additional licenses versus cumulative compliance platform license fees over three years

Why Heartland

No parallel structures

C5, ISO 27001 and DIN EN 50600 in one integrated control system.

No additional software

We work in your existing tools and systems.

One point of contact through to the report

From the gap analysis to alignment with the auditor.

Heartland NIS-2 ISMS - Umfassende SIcherheit
Heartland NIS-2 ISMS - Software Freiheit
Heartland NIS-2 ISMS - Neue Wertschöpfung
Heartland NIS-2 ISMS -  keine Folgekosten
Heartland NIS-2 ISMS - in weniger als 4 Monaten

The auditor’s perspective from day one

We build what the auditor wants to see.

Data center experience

DIN EN 50600 and ISO 27001 for colocation and AI data centers.
From infrastructure to attestation –
in a clear hierarchy.
DIN EN 50600 secures the infrastructure, ISO 27001 the management system – the C5 attestation for your cloud service builds on both.
Ebene 1 Infrastruktur: DIN EN 50600 Zertifikat für Verfügbarkeit, Redundanz und physische Sicherheit im Rechenzentrum
DIN EN 50600 delivers:
PS
OPS
BCM
Ebene 2 Managementsystem: ISO 27001 Zertifikat einer akkreditierten Zertifizierungsstelle
ISO 27001 covers:
OIS
SP
HR
AM
SSO
SIM
COM
Ebene 3 Cloud Service: C5:2026 Testat Typ 2 mit 168 Kriterien, Systembeschreibung und Wirksamkeitsprüfung
C5-specific – we build it with you:
IAM
CRY
COS
PI
DEV
PSS
INQ
GC
From ISO 27001 to C5:2026
What your ISO 27001 already covers – and what C5:2026 newly requires
An existing certification covers the core but does not replace any C5 criterion.
Your basis · ISO 27001
C5 requires an ISO 27001-compliant ISMS (OIS-01); a stricter additional criterion requires a valid certification.
+ Cloud hardening
+ Tenant isolation
+ Transparency disclosures
+ Customer controls
New in C5:2026
C5:2026 replaces C5:2020 – with stricter requirements for identities, cryptography and development. Plus 6 General Conditions covering legal matters, availability, subservice organizations and data locations.
Shared Security Responsibility Model
Threat Intelligence
Confidential Computing
Container Management
168
17
6
3
Criteria
Criteria domains
General Conditions
Criteria types: Basic · AS · AC
Not a certificate but an attestation: the auditor decides whether each criterion is met. Heartland combines ISO 27001 and C5 in one control system.
Heartland solutions
Your partner for cloud security under BSI C5.